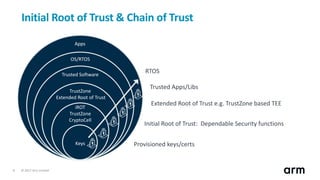
Relying parties are configured to belief specific root certificates, and that belief is what makes the rest of the chain meaningful. The Microsoft Root Certificates Program supports the distribution of root certificates, enabling clients to belief Home Windows products. Safe boot makes use of a hardware root of belief to check firmware and software program integrity before anything executes. An HSM or TPM holds the signing keys that validate each stage of the boot process, from firmware through the operating system loader.
Rather than possessing the obligatory 384 bits of pseudo-random security, several non-public keys evaluated single-digit and double-digit integers. This misconfiguration allows an attacker with the private key of any of the compromised intermediate CAs to impersonate any website or service. Six of the TLS certificates, trusted by Chrome, Mozilla, and Apple have been blocked by these distributors already. Two other certificates, used for codesigning by Microsoft, have also been blocked. Talos expects there shall be additional patches available throughout a variety of technologies as software program functions work to remediate the certificates’ exposure. Since December 2017, all GeoTrust certificates are issued beneath DigiCert’s trusted root certificates.
Simplified Tls Certificate Administration
- The NSS root certificates store is not solely utilized in Mozilla products such as the Firefox browser, but can additionally be utilized by different firms in a variety of merchandise.
- See how SailPoint sets the usual for identity security-helping enterprises cut back risk, scale with confidence, and keep ahead of what’s next.
- The hierarchical trust mannequin scales effectively, supporting millions of certificates via a relatively small variety of belief anchors.
- NHIDR is a proactive protection mechanism that constantly displays machine identity conduct.
Each of the lively intermediates above documents which chain is offered by default, and which (if any) extra chains may be requested by ACME clients. In basic, chains which terminate at ISRG Root X1 have the most important size but additionally the greatest compatibility with older purchasers. Chains which terminate at ISRG Root X2 (only supplied for ECDSA certificates) are smaller, but will solely work with clients that have received an replace to their belief store after 2022 or so. Chains which terminate at Root YE or Root YR are not expected to work with any of the most important belief shops, as these https://ondcashadvanceonline.com/free-software-and-online-training-resources-for-internet-developers/ roots have not yet been incorporated. For additional information on the compatibility of our root certificates with various gadgets and belief stores, see Certificate Compatibility.
Secure Infrastructure
Enclaves carry a decrease assurance stage than a FIPS-validated HSM, which makes them a match for app-level protections while enterprise key management stays with dedicated hardware. Each cryptographic key a company relies on has to be generated and stored somewhere. If a software keystore runs on the identical server as the application it protects, the secret’s solely as secure as the operating system round it. Root CAs utilize Hardware Security Modules (HSMs) to guard cryptographic keys. HSMs provide tamper-resistant storage for the Root CA’s non-public key, safeguarding it towards unauthorized entry and tampering.
Organizations should assess TLS-using software and appliances, together with proxies, reverse load balancers, VPN shoppers, and gateways. Publicity is determined by the certificates chain being validated and the belief store and revocation conduct in use. A stale or separately managed belief store might have an software, operating-system, firmware, or trust-bundle update; verify the required motion for each product. Not Like languages that defer completely to exterior dynamic system libraries (like OpenSSL), the Go programming runtime implements its personal X.509 chain verification engine in the standard library (crypto/x509). Whereas Go often queries platform certificates, several platforms or static container environments depend on embedded or legacy root certificate pools where certificates revocations are ignored.
Safe Mail Root Certificates
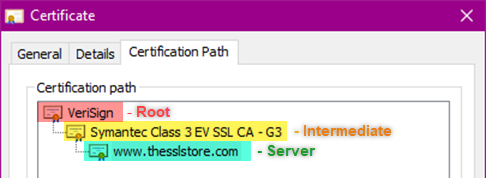
I’ve avoided utilizing that term too much till now as a result of it appears very summary till you drill down into the specifics slightly bit. It can problem certificates instantly, making it a lot simpler to deploy certificates and simplifying installation. It’s an intermediate certificate, however, as a end result of the Sub CA doesn’t have its personal trusted root is has to chain to a third-party CA that does have one. A root certificate is invaluable, because any certificates signed with its personal key shall be automatically trusted by the browsers. Ergo, you actually need to be positive to can belief the Certificate Authority issuing from it.

Talos has identified “ARToken,” a phishing-as-a-service platform that targets Microsoft 365. The ARToken panel exposes 80+ API endpoints for system code phishing, Main Refresh Token persistence, e-mail entry, BEC operations, and SharePoint exfiltration. Yes, our Root CA options could be personalized to satisfy the distinctive safety necessities of different industries. We perceive that every trade faces particular challenges and threats, and our team is provided to tailor an answer that most closely fits your sector’s needs.